
RISK
is inevitable
ignorance is optional

RESILIENCE
preparation
&
awareness
built on
built on

PHISH
Don't
feed the

DEFENCE
small discoveries
begins with

SECURITY
it’s a continuous
journey
isn’t a destination
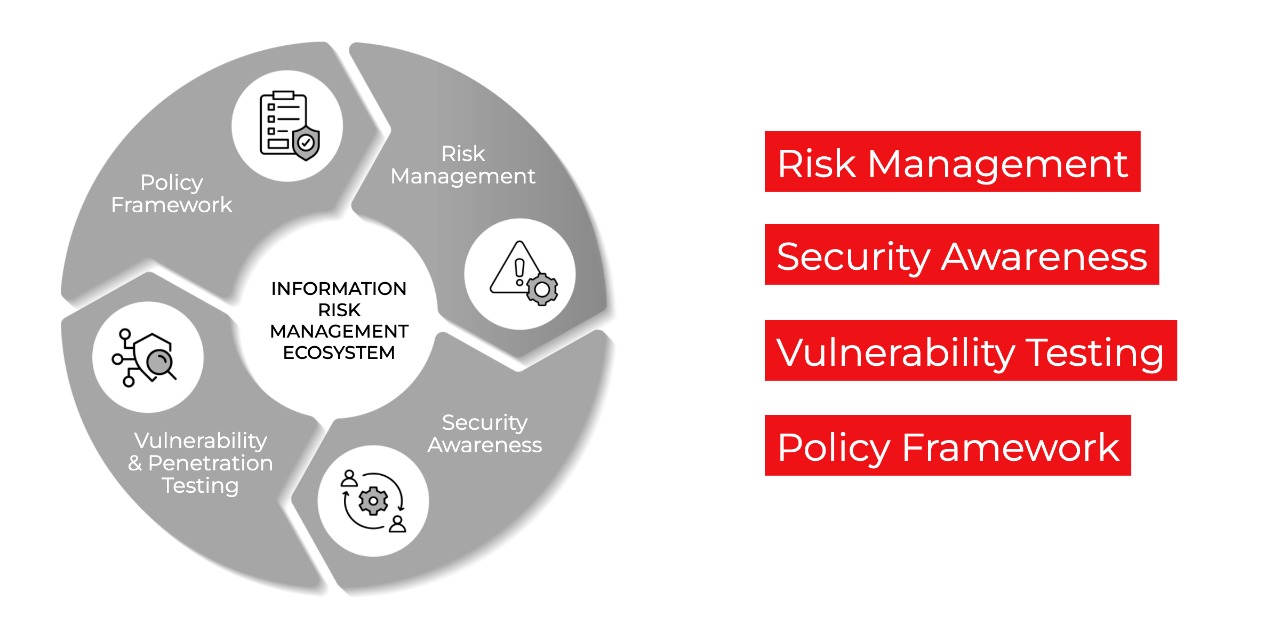
Rsecure specialises in Information Risk Management, helping organisations build and maintain a resilient and business-aligned security framework.

Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM

Management leveraging policy shortfall and policy
execution as a starting point, ensuring the identification,
categorization, and continuous management of
information risks across the business.
We provide guidance and support in undertaking
comprehensive risk assessments to uncover
vulnerabilities, classify risks based on impact and
likelihood, and align them with regulatory and business
priorities. We consult on risk treatment strategies,
including mitigation, transfer, acceptance, or
avoidance, integrating them into an ongoing Risk
Management Framework.
This framework ensures risks are continuously
monitored, reviewed, and adapted to evolving threats,
supported by governance controls, incident response
planning, and compliance tracking. By embedding risk
management into daily operations, we help businesses
reduce exposure, improve resilience, and meet regulatory
and insurer expectations with clear, actionable insights.

Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM

and continuous review aligned with ISO 27001:2022
standards, ensuring the secure management
of information.
Our approach helps organisations
develop, refine, and contextualize their policy
repository to meet internationally recognised
security controls.
We focus on effective policy communication,
awareness, and implementation, including
monitoring, evidence gathering, and regular
reviews to maintain resilience against
evolving threats.

Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM

Awareness Training and Policy Awareness Training,
equipping employees with the knowledge to
recognise cyber risks and understand implemented
security policies.
Designed to address compliance obligations, our
program provides contextual, role-specific training
that enhances security culture while ensuring
regulatory and insurer requirements are met.
Key components include phishing simulations,
customised policy awareness training, and traditional
cybersecurity education, all backed by evidence-
based tracking to demonstrate compliance and
risk mitigation efforts.
Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM
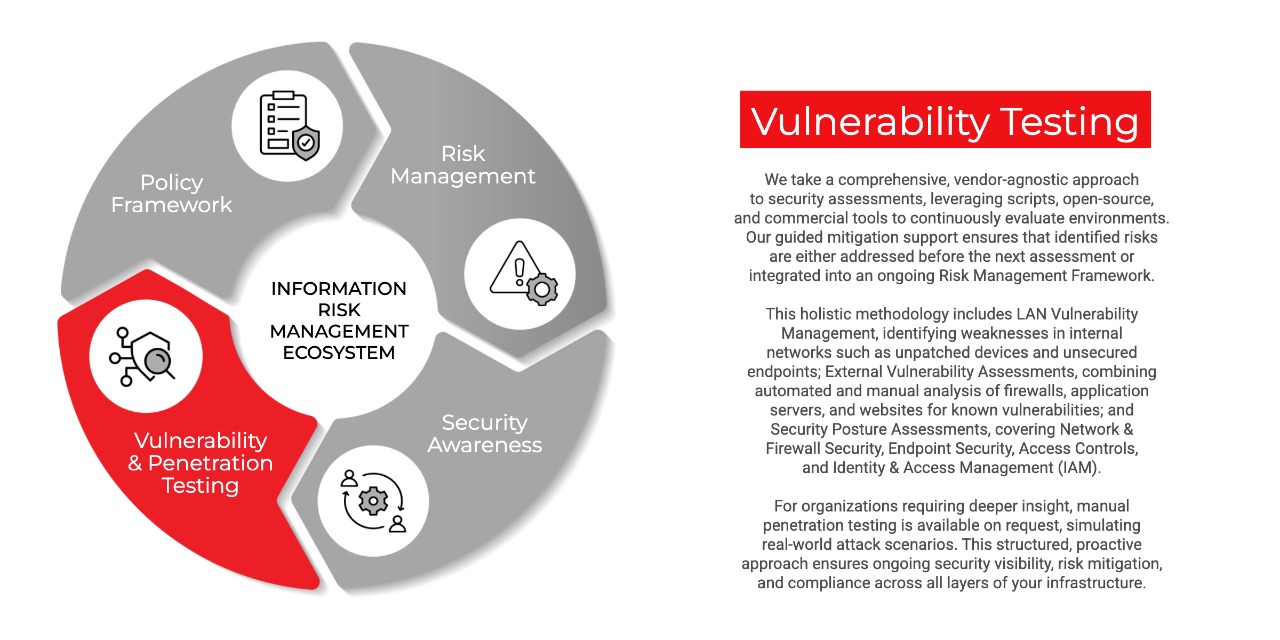
to security assessments, leveraging scripts, open-source,
and commercial tools to continuously evaluate environments.
Our guided mitigation support ensures that identified risks
are either addressed before the next assessment or
integrated into an ongoing Risk Management Framework.
This holistic methodology includes LAN Vulnerability
Management, identifying weaknesses in internal
networks such as unpatched devices and unsecured
endpoints; External Vulnerability Assessments, combining
automated and manual analysis of firewalls, application
servers, and websites for known vulnerabilities; and
Security Posture Assessments, covering Network &
Firewall Security, Endpoint Security, Access Controls,
and Identity & Access Management (IAM).
For organizations requiring deeper insight, manual
penetration testing is available on request, simulating
real-world attack scenarios. This structured, proactive
approach ensures ongoing security visibility, risk mitigation,
and compliance across all layers of your infrastructure.
Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM
Framework
Management
Awareness
& Penetration
Testing
RISK
MANAGEMENT
ECOSYSTEM
leveraging policy shortfall and policy execution as a starting
point, ensuring the identification, categorisation, and
management of information risks across the business.
We provide guidance and support in undertaking
comprehensive risk assessments to uncover vulnerabilities,
classify risks based on impact and likelihood, and align
them with regulatory and business priorities. We consult on
risk treatment strategies, including mitigation, transfer,
acceptance, or avoidance, integrating them into an ongoing
Risk Management Framework.
This framework ensures risks are continuously monitored,
reviewed, and adapted to evolving threats, supported by
governance controls, incident response planning, and
compliance tracking. By embedding risk management into
daily operations, we help businesses reduce exposure,
improve resilience, and meet regulatory and insurer
expectations with clear, actionable insights.
Framework
Awareness
RISK
MANAGEMENT
ECOSYSTEM
Management
& Penetration
Testing
and continuous review aligned with ISO 27001:2022
standards, ensuring the secure management
of information.
Our approach helps organisations
develop, refine, and contextualize their policy
repository to meet internationally recognised
security controls.
We focus on effective policy communication,
awareness, and implementation, including
monitoring, evidence gathering, and regular
reviews to maintain resilience against
evolving threats.
Framework
Awareness
RISK
MANAGEMENT
ECOSYSTEM
Management
& Penetration
Testing
Awareness Training and Policy Awareness Training,
equipping employees with the knowledge to
recognise cyber risks and understand implemented
security policies.
Designed to address compliance obligations, our
program provides contextual, role-specific training
that enhances security culture while ensuring
regulatory and insurer requirements are met.
Key components include phishing simulations,
customised policy awareness training, and traditional
cybersecurity education, all backed by evidence-
based tracking to demonstrate compliance and
risk mitigation efforts.
Framework
Awareness
RISK
MANAGEMENT
ECOSYSTEM
Management
& Penetration
Testing
to security assessments, leveraging scripts, open-source,
and commercial tools to continuously evaluate environments.
Our guided mitigation support ensures that identified risks
are either addressed before the next assessment or
integrated into an ongoing Risk Management Framework.
This holistic methodology includes LAN Vulnerability
Management, identifying weaknesses in internal
networks such as unpatched devices and unsecured
endpoints; External Vulnerability Assessments, combining
automated and manual analysis of firewalls, application
servers, and websites for known vulnerabilities; and
Security Posture Assessments, covering Network &
Firewall Security, Endpoint Security, Access Controls,
and Identity & Access Management (IAM).
For organizations requiring deeper insight, manual
penetration testing is available on request, simulating
real-world attack scenarios. This structured, proactive
approach ensures ongoing security visibility, risk mitigation,
and compliance across all layers of your infrastructure.
Framework
Awareness
RISK
MANAGEMENT
ECOSYSTEM
Management
& Penetration
Testing
WHO WE ARE
Our executive team has a 30 year track record in IT support services, system administration, IT environment management, architecture and design.
Our staff include certified ISO27001 practitioners and specialists in policy formulation. We look forward to joining you on the Information Risk Management journey.
We have experience across multiple industry categories and have facilitated General Policy Frameworks, Incident Management Solutions, POPIA compliance as well as FSCA Joint Standard Readiness spanning major financial institutions to small and medium business with tighter budgets but the same compliance overhead.
Rsecure – Our approach is built on four core pillars that define a healthy and effective information security system:
1. Policy Framework Development
A well-defined Policy Framework is the foundation of strong information security. We assist in the formulation, adoption, and ongoing management of security policies, ensuring alignment with industry standards such as ISO 27000, while being mindful of local legislation and regulatory requirements that encompass POPIA and PAIA obligations. Our policies are designed to be practical, actionable, and adaptable to your organisation’s unique needs.
2. Risk Management
Effective risk management goes beyond compliance—it integrates policies, systems, and people into a Risk Management Framework that identifies, assesses, and mitigates security risks. We help organisations build structured, sustainable processes to manage risk proactively.
3. Security Awareness & Training
Security is only as strong as the people who uphold it. Our Security Awareness programs go beyond standard cyber risk training and phishing simulations. We emphasise contextual awareness—ensuring employees understand how policies affect their roles and how they contribute to a secure organisation. Our approach fosters a culture where security is not just a requirement but a shared responsibility.
4. Vulnerability Assessments & Continuous Monitoring
Understanding your security posture requires ongoing assessment and improvement. Traditional manual penetration testing can be costly and disruptive, which is why we focus on continuous scanning and monitoring of both internal networks and external attack surfaces. Our monthly reports include detailed insights, remediation guidance, and compliance support, helping organisations stay ahead of evolving threats.

Complete the form below and we will contact you
